Operation Fractured Future: The Cybersecurity Training Game That Makes Every Decision Count
Operation Fractured Future is a SCORM-compatible cybersecurity training game that drops learners into four high-stakes crisis scenarios between 2024 and 2030, where every decision shapes the future. With live threat metrics, branching multi-stage incidents, and real consequences for every call you make, this is the security awareness module your organization has been waiting for.
By Nathan Stoker · Published Sep 27, 2026 · Updated Nov 8, 2026 · 9 min read
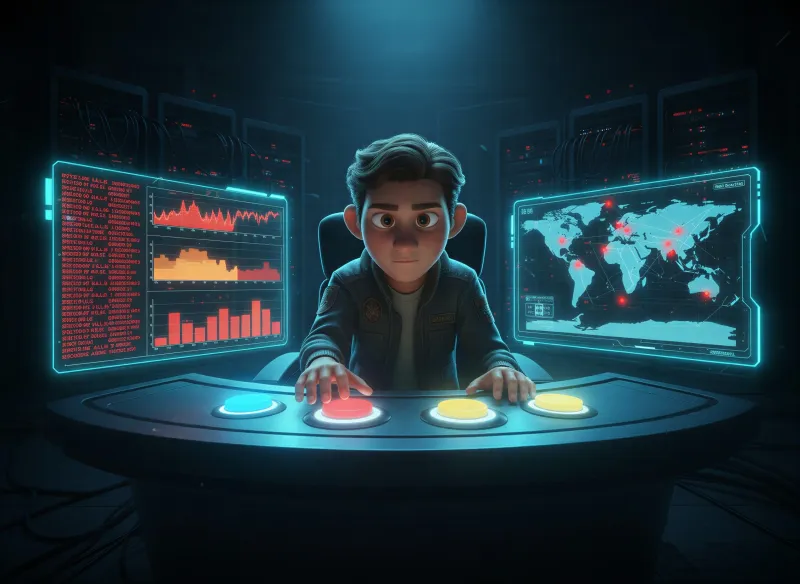
The future has already collapsed. Hospitals are dark. Banks are frozen. Power grids are failing. And somewhere between 2024 and 2030, a series of decisions (decisions your organization made) cracked the foundation of civilization.
Operation Fractured Future is a SCORM-compatible cybersecurity consequence simulator that puts learners inside the moments that matter. Not a quiz. Not a slide deck. A fully interactive crisis room where every choice ripples forward, delayed consequences surface later, and the only way out is through.
This is the e-learning your security awareness program has been missing, and it's available as a ready-to-deploy premium module.
What Is Operation Fractured Future?
Operation Fractured Future is a scenario-based cybersecurity training game built for deployment in any SCORM 1.2-compatible LMS. Learners are sent back through time via an "experimental temporal uplink" to relive four critical cybersecurity incidents between 2024 and 2030. Their decisions determine whether the future collapses or stabilizes.
This isn't gamification bolted onto a compliance checklist. The narrative framing is baked into every layer of the experience: the retro-cyberpunk visual aesthetic, the glowing threat metrics ticking down in real time, the Rewind Protocol that lets learners undo one catastrophic mistake, if they use it wisely.
Each incident is multi-stage. Make a bad call in Stage A, and Stage B transforms entirely. The consequences aren't hypothetical; they hit the live dashboard immediately.
Why Cybersecurity Training Has a Problem (And Why This Fixes It)
Traditional security awareness training has a completion problem and a retention problem. Learners click through slides, pass a multiple-choice quiz with a score of 80%, and return to their desks having forgotten everything by Thursday.
The research is clear: passive learning doesn't produce behavioral change. Decision-based simulation does.
Operation Fractured Future forces learners to experience the cost of a wrong decision, not just read about it. When a learner chooses to rush a vendor payment at quarter-end and $47,000 disappears to an offshore account in real time, that moment becomes a memory anchor. The emotional weight of watching those financial metrics collapse does what a bullet point about "BEC fraud" never could.
The game also teaches the nuance that compliance training ignores. In real cybersecurity situations, there isn't always a clearly "correct" answer. Sometimes you patch immediately and break payroll. Sometimes you monitor for lateral movement and the attacker steals your entire Active Directory. Fractured Future puts learners inside those trade-offs and lets them feel the weight.
The Four Incidents: What Learners Will Face
Incident 1: The Trusted Vendor
A long-time software vendor sends an urgent invoice update. Quarter-end. Finance is pushing hard. The email looks almost right.
Learners must examine email headers, analyze domain registration dates, and read between the lines of a Helpdesk call from someone claiming to be the vendor's billing contact. The evidence is there (clues are surfaced interactively with hover tooltips), but the pressure to act fast is real.
The branching here is deep. A good early decision leads to a social engineering attempt via phone. A bad early decision triggers a live ransomware infection on the Finance VLAN. Learners who choose to "monitor quietly" to build a complete picture watch the entire employee payroll database exfiltrated in real time. That decision costs them 20 points each in Security and Public Trust simultaneously.
Incident 2: Patch Deferment
A CVSS 9.8 critical vulnerability with a published proof-of-concept sits unpatched on the authentication server. The VP of Operations will not allow the 3-hour downtime window during payroll processing.
This incident is a masterclass in competing priorities. Learners who patch immediately solve the security problem but trigger a legacy integration failure mid-payroll-run, and then face pressure to roll back the patch to restore operations. Learners who defer the patch watch exploitation begin in the wild exactly 48 hours later, with a 400% spike in scanning activity against their auth server.
Every path through Incident 2 has real costs. That's the point.
Incident 3: Insider Credential Anomaly
At 3:22 AM, an HR manager's credentials log in from Bucharest, Romania. The employee is on PTO in Florida. 2.4 GB is already leaving the network.
This incident is about the cost of hesitation. Learners who lock the account immediately face political blowback from the HR Director and CHRO, but the forensic data backs them up. Learners who deploy a honeytoken to "build a complete threat picture" watch the attacker pivot to four additional accounts and dump the entire Active Directory. Learners who call the employee for verification first let the exfiltration grow from 2.4 GB to 8.1 GB, capturing medical records that trigger mandatory HIPAA notification requirements.
The delayed consequence system shines here: choosing to suppress the incident internally doesn't hurt immediately. It surfaces as regulatory fines and a class-action lawsuit one incident later.
Incident 4: Hospital Network Instability
Ransomware is encrypting patient records at 500 MB per second. The ER can't access allergy data. The CEO has sent a "Silence Protocol" email ordering you to keep the public-facing portals online because a merger is pending.
This is the most ethically complex incident in the game. Learners must weigh patient safety against operational continuity, choose between surgical isolation and full network shutdown, and decide whether to comply with a CEO directive that exposes them to personal liability under HIPAA.
The failover path reveals that the ransomware had been dormant in backups since August 29, six days before the attack. The last clean backup is three weeks old. Learners who restore from it lose three weeks of patient data. Learners who continue with the compromised backup face reinfection 36 hours later.
How the Game Engine Works
The Live Dashboard
Four metrics run across the top of every screen in real time: Infrastructure, Public Trust, Financial Stability, and Security Posture. Each begins at 85–90%, strong but not invincible. Every decision applies immediate or delayed effects to these metrics, and the bars animate visually so learners feel the impact of each choice.
The SCORM handler tracks session progress and saves the learner's position via cmi.core.lesson_location, enabling seamless LMS bookmark and resume functionality. Completion is recorded automatically when the final incident resolves.
Branching Stage Architecture
Each incident is not a single question with four answers. It is a multi-stage decision tree. Your answer to Stage A determines which Stage B you enter. Intermediate stages can route to different resolution paths, and some resolutions carry delayed consequences that surface in later incidents.
This is what separates Fractured Future from scenario-based slides. The game remembers what you did. A decision you made in Incident 1 can quietly reduce your Security score before Incident 3 even begins.
The Rewind Protocol
Learners begin with exactly two Rewind Tokens. Using a token rolls back the game state to the start of the previous decision point, not the entire incident, but the exact stage where the last choice was made.
This mechanic is pedagogically significant. It gives learners permission to make a mistake and learn from it, while keeping the tokens scarce enough that using them feels meaningful. Learners who exhaust both tokens early may face the consequences of a later catastrophic decision with no safety net.
The Temporal Network Map
An interactive network graph visualizes all four incidents as nodes, showing the learner's position in the timeline and the interconnected relationships between crises. It's accessible at any point from both the intro screen and the live dashboard.
The 2030 Outcome Convergence
The final screen isn't a summary table. It's a narrative outcome determined by the cumulative state of all four metrics. Learners who protected security at the cost of infrastructure but maintained public trust receive a different outcome title and story than learners who deferred every hard call.
Five outcomes are possible, from "Timeline Collapse" through "Partial Recovery" and "System Stabilized" to "Golden Age Restored", each with its own verdict on what the learner's decisions meant for the future.
Who This Is Built For
Cybersecurity Teams and SOC Analysts
The incident scenarios are drawn from real attack patterns: BEC fraud, patch management failures, SIM-swap credential theft, ransomware with backup contamination. The technical evidence (email headers, firewall logs, process trees, CVE reports) is accurate. This is not a watered-down awareness module. Analysts will recognize the situations and face genuinely difficult judgment calls.
Compliance and Security Awareness Programs
Operation Fractured Future covers the major categories that enterprise security awareness programs are required to address: phishing recognition, social engineering, patch management decision-making, insider threat response, and incident escalation procedures. The SCORM 1.2 packaging means it drops directly into any major LMS without configuration work.
Leadership and Decision-Makers
The game is specifically designed to put non-technical decision-makers inside situations where business pressure conflicts with security best practice. The VP who won't allow the patch window. The CEO who wants the breach suppressed for the merger. These aren't villains; they're characters learners may recognize from their own organizations. Fractured Future helps leadership feel the consequences of those trade-offs before a real incident forces them to.
The Visual Experience
Operation Fractured Future runs in a retro-cyberpunk aesthetic: near-black backgrounds, CRT scanline overlays, vignette effects, and a color system built around cyber blue (#00f0ff), critical red (#ff2a2a), and warning amber (#ffae00).
Typography uses Orbitron for headings and Share Tech Mono for all UI text, both chosen to reinforce the classified-terminal aesthetic of the experience. Evidence is presented in themed panels: email clients, terminal views, HR record viewers, and chat interfaces, each formatted to look like the real system it represents.
The result is a training experience that feels like a high-stakes operations center, not a learning module.
Technical Specifications
Format: SCORM 1.2 compatible
LMS Compatibility: Any SCORM 1.2 LMS (Cornerstone, Docebo, TalentLMS, Moodle, Blackboard, SAP SuccessFactors, and more)
Completion Tracking: Automatic; status set on game end, bookmark saved per incident
Runtime: Approximately 30–45 minutes (varies by decision path)
Device Support: Desktop and laptop (optimized for 1280px+ viewport)
Dependencies: None; all assets self-contained in the SCORM package
Scoring: Four-metric composite score mapped to letter grade (S, A, B, C, D, F)
Ready to Deploy Fractured Future in Your LMS?
Operation Fractured Future is available as a licensed SCORM package, ready to upload and assign. No development work required on your end.
What's included in the license:
SCORM 1.2 package (zip, ready to upload)
Facilitator guide with incident debriefs and discussion prompts
Pre/post assessment items tied to each incident's learning objectives
LMS setup documentation for common platforms
If you're running a security awareness program, building a cybersecurity curriculum, or looking for a flagship module that actually gets talked about after the training, this is the one.
Get in touch to request a demo or discuss licensing options.
Key Takeaways
Operation Fractured Future isn't just a cybersecurity training game. It's a consequence engine. Every decision learners make, including the ones they thought were safe, shapes the outcome of the timeline they're trying to save.
The multi-stage branching means no two learners have exactly the same experience. The delayed consequence system means good decisions don't always feel rewarding immediately, and bad decisions don't always announce themselves right away. That's not a design flaw. That's how real security incidents work.
For organizations serious about security awareness that sticks, Fractured Future delivers an experience that learners will remember, not because they were told to, but because they lived through the consequences of getting it wrong.
The future is watching. What will you decide?
Nathan Stoker
I build custom eLearning in Storyline, Rise and JavaScript, and I make the free tools and templates on this site. Need an interaction like this in your course? Let's talk.